
Code analysis and fixing
The programming errors left in Apache or Nginx logs, file by file, with each fix and the malware analysis. Premium version, with an executive security summary.
SW-COD-… 73 pages
Code audit
All its code, file by file. The errors, with the line where they are. The vulnerabilities, ordered by severity. And the web server logs, point by point. In a report the website owner understands and its technician can follow step by step.
Verdict: the website works, but a form allows uploading files without checking their type. Fix it first: the action plan has 6 steps.
Inside the SOC
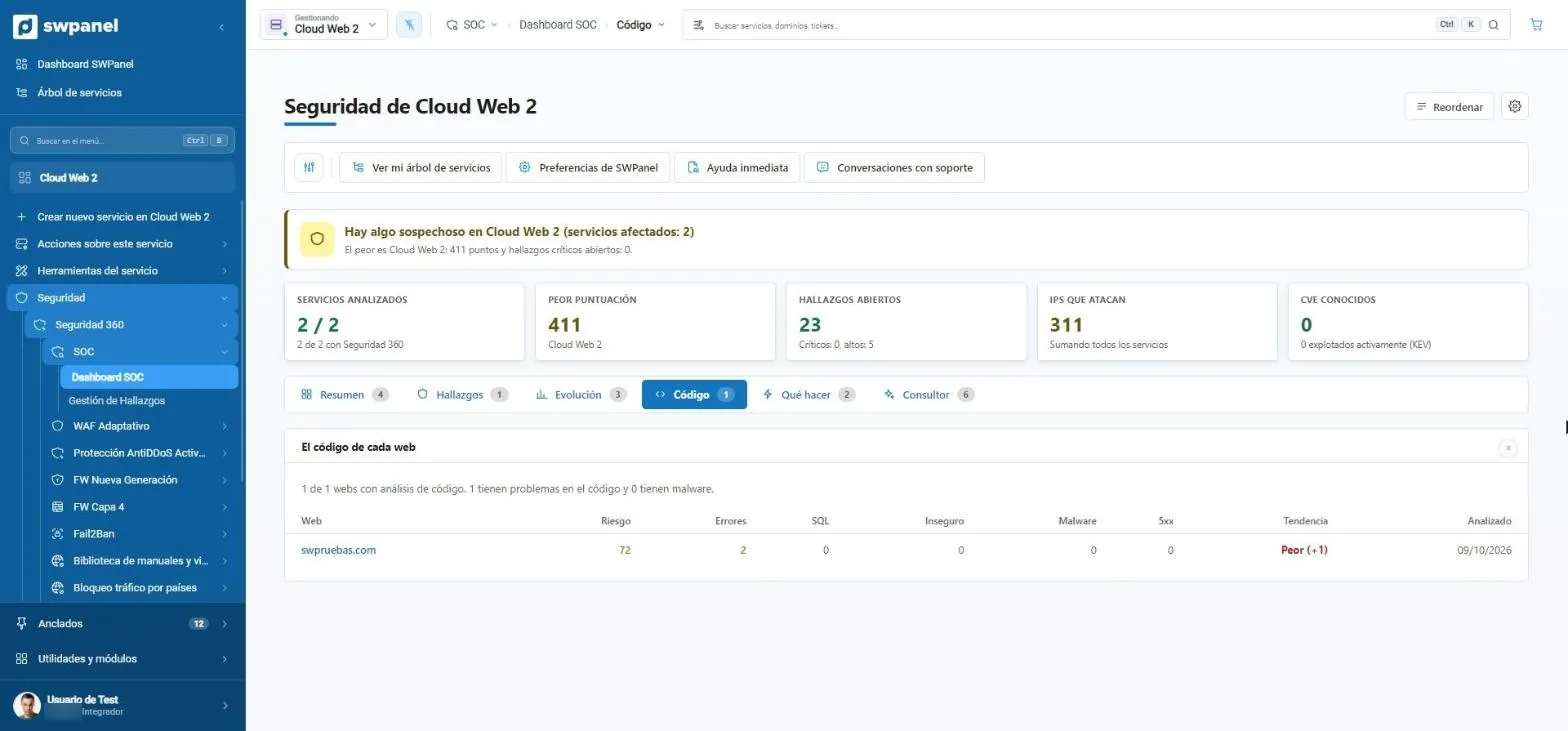
SOC › Code
The SOC scores each website's code every day. When risk rises, the code audit gives you the exact picture: file, line and how to fix it.
What it analyzes
Developer tools look at the repository, scanners look at malware and a pentest takes weeks. SWPanel's audit brings code, logs, malware and CMS together in a single report on the already-hosted website.
All the website's code, reviewed file by file.
Programming and runtime errors, with the file and line where they are.
The weak points of the code and installed software, ordered by severity.
Point by point: who comes in, what they request, what fails and what they try to attack.
The report
The security verdict, on one page.
Whether there's malicious code and how the content manager is doing.
What's happening on the web server.
What needs to change in each one.
Numbered, step by step.
Pages in plain language, with a section for their technician.
| Moment | What for |
|---|---|
| New customer | Entry audit: shows what state the website is in before proposing anything. |
| Migration or redesign | Know what comes along and what needs fixing before moving the website. |
| Incident | When a website fails or gets infected: what happened, where and how to fix it. |
| Periodic review | Check that the website is still clean and up to date. |
An example
A real code analysis and fix report on swpanel.com, with fictitious data. There are Premium and Standard versions.
The programming errors left in Apache or Nginx logs, file by file, with each fix and the malware analysis. Premium version, with an executive security summary.
SW-COD-… 73 pages

A service's security month: NGFW threats, SOC findings, blocked countries and bots, code analysis, adaptive WAF, what was done and next month's plan.
SW-S36-… 47 pages
What the NGFW detected and blocked in a period: by severity, type and origin, the changes over the last six months and what to do first.
SW-NGF-… 29 pages
Each document carries a unique number and token linking it to the original stored in SWPanel. How it's verified.
For partners
Nobody buys a monthly fee the first time. An audit with the exact picture of their website opens the conversation and prepares the sale of Security 360 and maintenance.
| Alternative | Market reference price |
|---|---|
| Malware and vulnerability scanners | €15 to €40 per month |
| Web pentest in Spain, limited scope | From €1,490 |
Market prices consulted on October 7, 2026, excluding VAT. Details and sources in the comparison.
Also for your code
Code Analyzer reviews your repository on every push. The Bulletin and the autopilot take care of what's already published.
The day's vulnerabilities, with your services inside. It tells you whether it affects you, what SWPanel does and what you have to do.
See the BulletinWhat SWPanel does on its own, every night. It blocks attacks, applies the safe things, asks you about the delicate ones and tells you every week.
Learn about the autopilotEvery push, reviewed before reaching your website. GitHub, GitLab, Gitea or Bitbucket, with the AI Engine fix and Pull Request.
See Code AnalyzerFrequently asked questions
Launch it from SWPanel and receive the report with its action plan.